How to setup Firewall on HiddifyManager panel
This page explains what a firewall is, how to turn on HiddifyManager's built-in firewall, and how to open a port by hand when a program that HiddifyManager does not know about needs one.
What is a firewall?
A firewall is software or hardware that controls which network traffic may reach a computer or server, and blocks the rest. Here we only deal with the software firewall on Linux servers.
On Linux, a common firewall tool is iptables. You give it a list of rules. Each rule says which traffic (for example, which port, a numbered "door" that a service listens on) is allowed through and which is blocked. HiddifyManager uses iptables.
The firewall in the HiddifyManager panel
HiddifyManager can manage the server's firewall for you. When it is on:
- Only the ports HiddifyManager needs stay open: SSH (port
22and the port your SSH server really uses),80,443,53, and every port your enabled proxies use (the same list that Public ports shows on the panel's Actions page). - All other incoming connections are blocked.
- Ping (ICMP) is still allowed, so you can still test whether your IP is clean.
- When you change a port or turn a proxy on or off in the panel, HiddifyManager updates the rules for you when you apply the changes.
The firewall is off by default. We recommend turning it on, because it makes your server harder to attack.
To turn it on:
- Log in to your HiddifyManager panel.
- In the sidebar, under Settings, click Settings, and find the General Settings card. You can also type
Firewallin the settings search box. - Turn on Firewall.
- Click Save, and apply the changes when the panel asks you to.
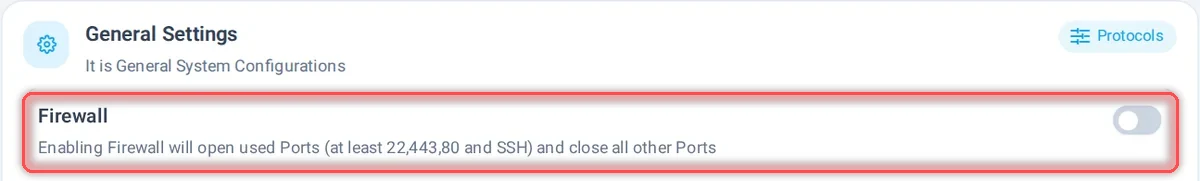
Before you turn it on
If you run other programs on the same server that need their own ports (for example another panel or a web server), open those ports by hand first, as shown below. Otherwise they stop working once the firewall is on.
Open a port by hand
Do this only for programs that HiddifyManager does not manage. HiddifyManager opens the ports of its own proxies by itself.
Before you start, connect to your server over SSH (a secure way to type commands on a remote server). If you don't know how, see How to connect to the server via SSH. If the HiddifyManager menu opens, press Cancel (or Esc) to close it. If the menu is still on the screen, type clear and press Enter.
-
Run this command on your server, over SSH. This example opens TCP port
1234. Replace1234with the port number you need:If the program uses UDP, run the same command with
-p udpinstead of-p tcp. If your server uses IPv6, run the same command again withip6tablesinstead ofiptables. -
Check that the rule was added:
You should see a line with
ACCEPTanddpt:1234(your port). -
Save the rules so they survive a reboot:
If the command is not found, install it with
apt install iptables-persistentand run it again.
Block ping (optional)
HiddifyManager's firewall rules always allow ping. Most people should leave it that way, because ping helps you check whether your server is reachable. If you still want to block ping, run this on your server, over SSH:
To allow ping again, remove that rule:
Remember that online ping tests will fail while ping is blocked. Use a TCP test on port 443 instead.
Troubleshooting
- You can't connect over SSH after turning on the firewall: HiddifyManager opens port
22and the port your SSH server is using when the firewall rules are applied. If you changed the SSH port afterwards, apply the panel's configuration again, or log in through your hosting provider's web console and runhiddify apply. - Another program on the server stopped working: its port is closed. Open it by hand as shown above.
- A port you opened by hand is closed again after a reboot: you did not save the rules. Run
netfilter-persistent save.